Kevin Roleke
[email protected]
github.com/kevinroleke
Earlier this evening my friend asked if I knew anything about a hosting provider called PRQ. In fact I did; PRQ is a Swedish free-speech-absolutist hosting company run by two of the The Pirate Bay founders.
While staring at the PRQ website on my laptop, amazed that it's still in operation, still preaching its original ethos, it suddenly hit me:
Remember when The Pirate Bay BGP hijacked North Korea?
As one can imagine, it's pretty damn hard to find an ISP willing to host such a high profile piracy service. During its heyday, The Pirate Bay had to constantly migrate between new upstream providers and domain names, as copyright holders and industry organizations like the MPAA and RIAA were vigilant to pressure ISPs and registrars to cut off its hosting. Part of what cemented The Pirate Bay's legendary status was its ability to always come back online and rise out of the ashes of a DMCA strike like a phoenix. Case in point, it's still online to this day, having just celebrated its 23rd birthday in September.
From late 2012 up through Feburary 2013, connectivity to TBP was being provided by an affiliated ISP named Serious Tubes Networks (which is curiously also still online and offering VPS hosting). Facing a lawsuit from Rättighetsalliansen, an anti-piracy organization funded by the MPAA, the Swedish Piratpartiet, which ostensibly was hosting the TBP via Serious Tubes, opted to cease providing refuge for the site that Feburary. Instead, the bandwidth would be supplied by the Norweigan and Catalan pirate parties.
One week into this new (supposed) hosting arrangement, in March 2013, the Norweigan Pirate Party (supposedly) cut off TBP once more. Only this time, instead of coming back under the aegis of yet another European pirate party, it seems North Korea had stepped in and offered TBP virtual asylum.
PRESS RELEASE, NEW PROVIDER FOR TPB
FOR IMMEDIATE RELEASE, 3 MARCH 102, 평양 (PYONGYANG).
The Pirate Bay has been hunted in many countries around the world. Not for illegal activities but being persecuted for beliefs of freedom of information. Today, a new chapter is written in the history of the movement, as well as the history of the internets.
A week ago we could reveal that The Pirate Bay was accessed via Norway and Catalonya. The move was to ensure that these countries and regions will get attention to the issues at hand. Today we can reveal that we have been invited by the leader of the republic of Korea, to fight our battles from their network.
This is truly an ironic situation. We have been fighting for a free world, and our opponents are mostly huge corporations from the United States of America, a place where freedom and freedom of speech is said to be held high. At the same time, companies from that country is chasing a competitor from other countries, bribing police and lawmakers, threatening political parties and physically hunting people from our crew. And to our help comes a government famous in our part of the world for locking people up for their thoughts and forbidding access to information.
We believe that being offered our virtual asylum in Korea is a first step of this country's changing view of access to information. It's a country opening up and one thing is sure, they do not care about threats like others do. In that way, TPB and Korea might have a special bond. We will do our best to influence the Korean leaders to also let their own population use our service, and to make sure that we can help improve the situation in any way we can. When someone is reaching out to make things better, it's also ones duty to grab their hand.
Sure enough, if you ran a traceroute on thepiratebay.se you would see the final hop was indeed an IPv4 address assigned to the hermit kingdom.
 3 at-grz-lazg-pe02-vl-2084.upc.at (84.116.229.73) 15.597 ms -> Graz, Austria
 4 at-vie15a-rd1-vl-2032.aorta.net (84.116.228.85) 18.448 ms -> Vienna, Austria
 5 de-fra01a-rd3-xe-2-1-0.aorta.net (213.46.160.69) 18.414 ms -> Frankfurt, Germany
 6 84.116.132.174 (84.116.132.174) 16.739 ms -> Frankfurt, Germany
 7 xe-0.de-cix.frnkge03.de.bb.gin.ntt.net (80.81.192.46) 82.919 ms -> Frankfurt, Germany
 8 ae-1.r02.frnkge03.de.bb.gin.ntt.net (129.250.4.163) 21.954 ms -> Frankfurt, Germany
 9 xe-3-2.r00.dsdfge02.de.bb.gin.ntt.net (129.250.5.61) 20.299 ms -> Frankfurt, Germany
 10 213.198.77.122 (213.198.77.122) 20.850 ms -> Frankfurt, Germany
 11 * * *
 12 xe-0-1-0-3.r02.frnkge03.de.bb.gin.ntt.net (129.250.5.62) 68.594 ms -> Frankfurt, Germany
 13 xe-0.level3.frnkge03.de.bb.gin.ntt.net (129.250.8.202) 72.588 ms -> Frankfurt, Germany
 14 vlan90.csw4.Frankfurt1.Level3.net (4.69.154.254) 154.316 ms -> Frankfurt, Germany
 15 ae-82-82.ebr2.Frankfurt1.Level3.net (4.69.140.25) 152.129 ms -> Frankfurt, Germany
 16 ae-61-61.csw1.NewYork1.Level3.net (4.69.134.66) 125.457 ms -> New York City, NY, USA
 17 ae-21-70.car1.NewYork1.Level3.net (4.69.155.67) 127.892 ms -> New York City, NY, USA
 18 INTELSAT-IN.car1.NewYork1.Level3.net (64.156.82.14) 176.317 ms -> New York City, NY, USA
 19 209.159.170.215 (209.159.170.215) 199.726 ms -> New York City, NY, USA
 20 * 202.72.96.6 (202.72.96.6) 694.793 ms -> Phenom Penh, Cambodia
 21 * * 175.45.177.217 (175.45.177.217) 803.654 ms -> Pyongyang, North Korea
 22 -> Dead.
Now, obviously this was a hoax of sorts; North Korea was not hosting The Pirate Bay, at least not willingly. At the time, a few different theories were proposed as to what exactly was going on here.
Initially, a BGP hijacking of the 175.45.177.0/24 block belonging to the North Korean state ISP Star Joint Venture (AS131279) seemed likely, as RPKI was not yet available at the time to secure the routing table. In 2013, announcing any IPv4 block as your own was easily accomplished by forging an LOA and handing it to your upstream.
Though, as it turns out, my memory was only half correct. No unauthorized BGP announcement had been made, rather TBP had began spoofing ICMP responses, allowing it to insert arbitrary hops into the traceroute data. They likely deployed fakeroute, a tool released by 2009 designed to do this exact thing.
Slightly disappointed by this reality, I opted to check on the historical routing data for 175.45.177.0/24 anyway, and to my surprise, found something very interesting:
The same block actually WAS hijacked about a year prior in April 2012, but not by The Pirate Bay. At 04:25:38 UTC on April 13, a Hong Kong ISP called CypressTel (AS131274) began announcing 175.45.177.0/24.
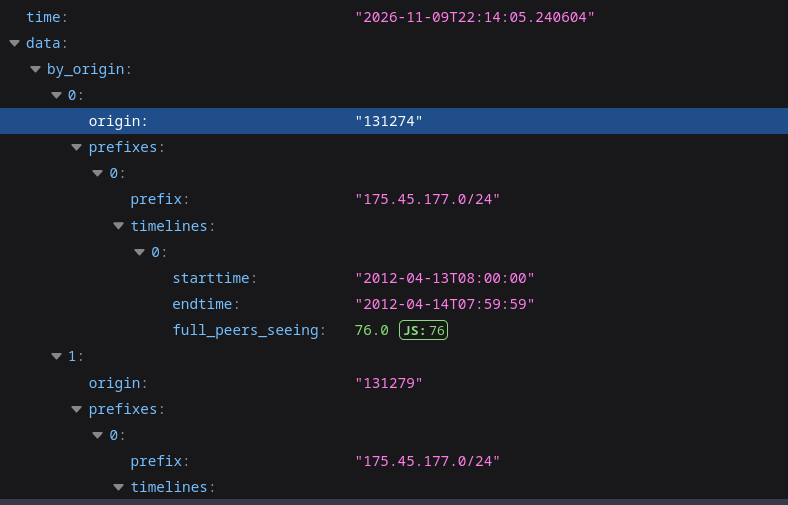
What was CypressTel doing here and why? I don't know for sure but here are some curious points:
Could this have been the result of a typo? I can't imagine a scenario in which some operator mistypes an ASN and it results in an unauthorized announcement of just one of the victim ASN's prefixes. Was it a pure coincidence that the aforementioned ASNs are only one digit off?
Was CypressTel involved in some legitimate manor with the addition of North Korea's Intelsat link?
If the hijacking was indeed intentional, what could someone stand to gain from taking over North Korean IP space beyond hacker bragging rights?
For the time being, I'm personally unable to make sense of this situation. Hoping that someone with a background in network engineering/telecommunications can chime in with a coherent theory; I will update this post accordingly.